
Data Destruction and the Telecommunications Act
How the Telecommunications Act and the data retention scheme affect disposal of network equipment, servers and storage, and what to check before telecommunications data is destroyed.
How the Telecommunications Act and the data retention scheme affect disposal of network equipment, servers and storage, and what to check before telecommunications data is destroyed.
The regulatory, legal, reputational and commercial consequences Australian organisations face when old IT equipment leaves with data still on it, and the steps that prevent them.
What has changed for data destruction in Australia since 2024, from APP 11.3 and PCI DSS v4.x to ISO 27001:2022 and NIST SP 800-88 Rev. 2, and what organisations should do now.
Data destruction processes drift over time. An annual audit of policy, process, records and providers catches gaps early. Here is what to include, how to test it and how to report findings.
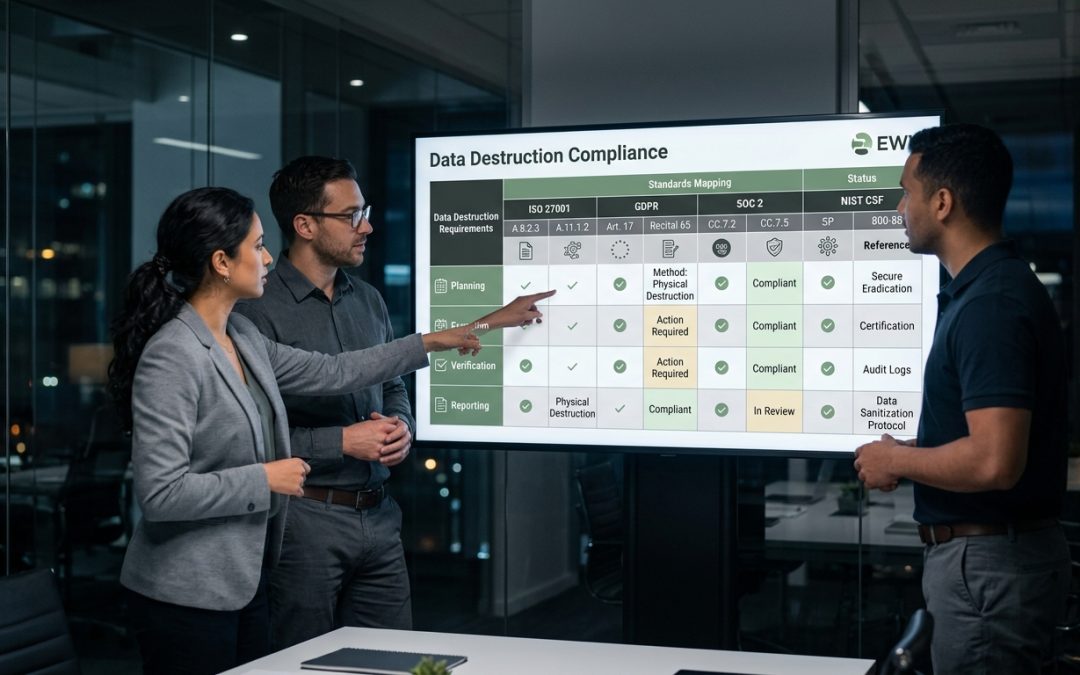
How the Privacy Act, ISO 27001, PCI DSS, APRA CPS 234, the ASD ISM, NIST SP 800-88 and GDPR each treat data destruction, and how one disposal process can satisfy them together.
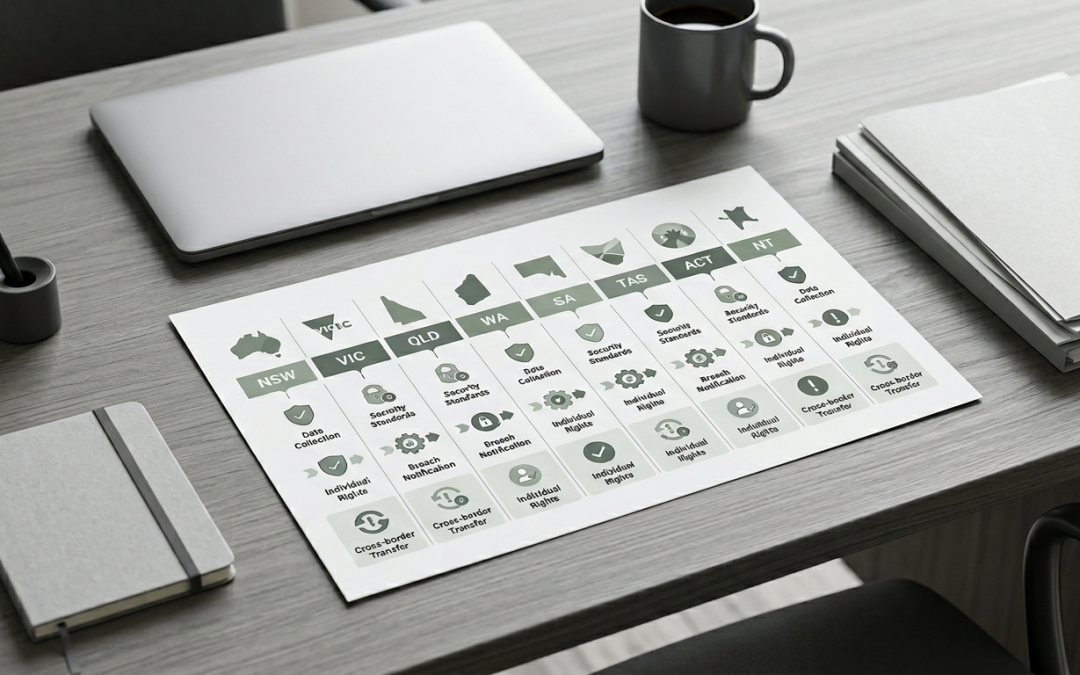
A summary of the state and territory privacy and health records laws that affect IT disposal, who they apply to, and how multi-state organisations can meet them with one process.