
The Australian Privacy Principles and IT Disposal
How APPs 1, 6, 8, 11, 12 and 13 apply when you retire IT equipment, what reasonable steps for destroying personal information look like, and how disposal links to the NDB scheme.
How APPs 1, 6, 8, 11, 12 and 13 apply when you retire IT equipment, what reasonable steps for destroying personal information look like, and how disposal links to the NDB scheme.
Where personal liability for directors can arise when retired IT equipment causes a data breach, the situations that increase exposure, and the governance steps that protect boards.
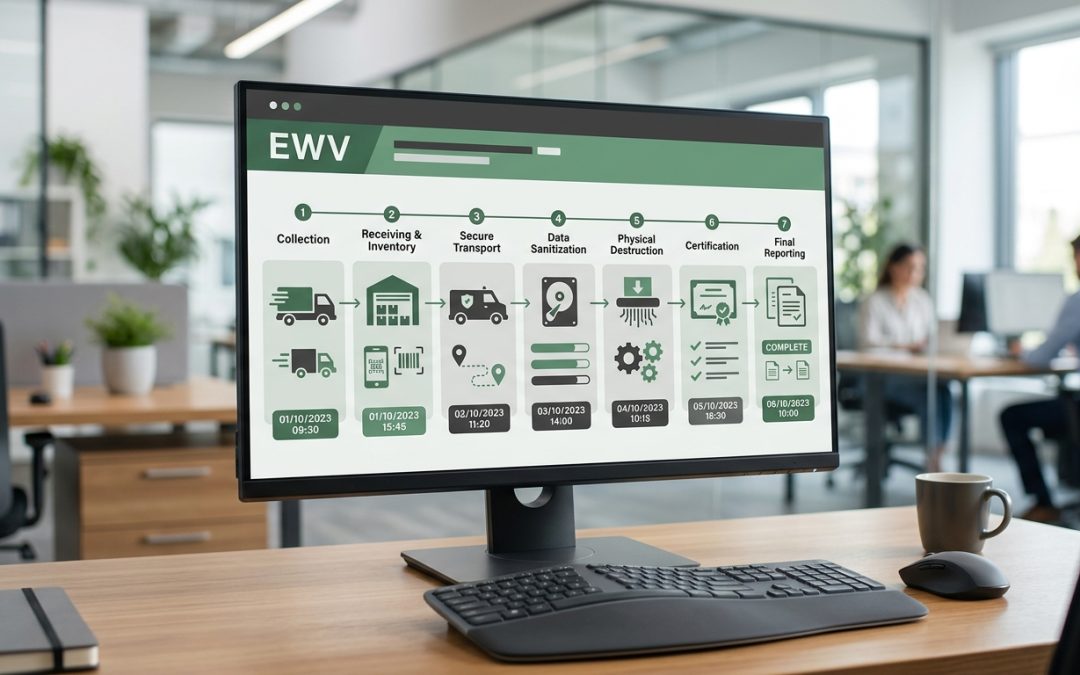
Auditors want evidence, not assurances. Learn what an IT disposal audit trail should contain, what ISO 27001, PCI DSS, the Privacy Act and CPS 234 focus on, and the gaps auditors find most.
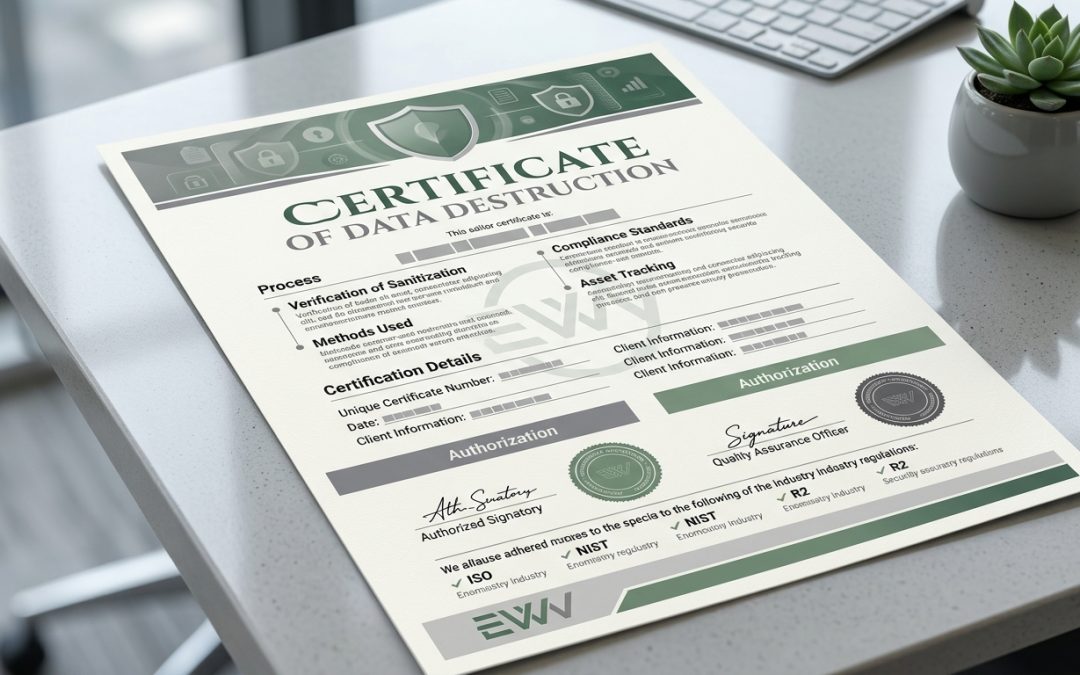
A certificate of destruction is your evidence that retired devices were properly sanitised. Learn what a good record should include, the red flags to watch for, and how to ask for better records.
What a legal hold is, why devices under hold must be pulled from the disposal queue, the consequences of destroying held data, and how to build hold checks into your IT disposal process.
How data sovereignty rules follow data onto retired devices, the disposal practices that can move restricted data offshore, and the controls that keep it within the required jurisdiction.