
APRA CPS 234 and Data Destruction Requirements
How APRA CPS 234 applies when banks, insurers and super funds retire IT equipment: asset classification, outsourced disposal, APRA notification timeframes and what internal audit should test.
How APRA CPS 234 applies when banks, insurers and super funds retire IT equipment: asset classification, outsourced disposal, APRA notification timeframes and what internal audit should test.
How the ASD Essential Eight and the Information Security Manual apply when you retire IT equipment, from patching and credential revocation to sanitisation methods and disposal records.
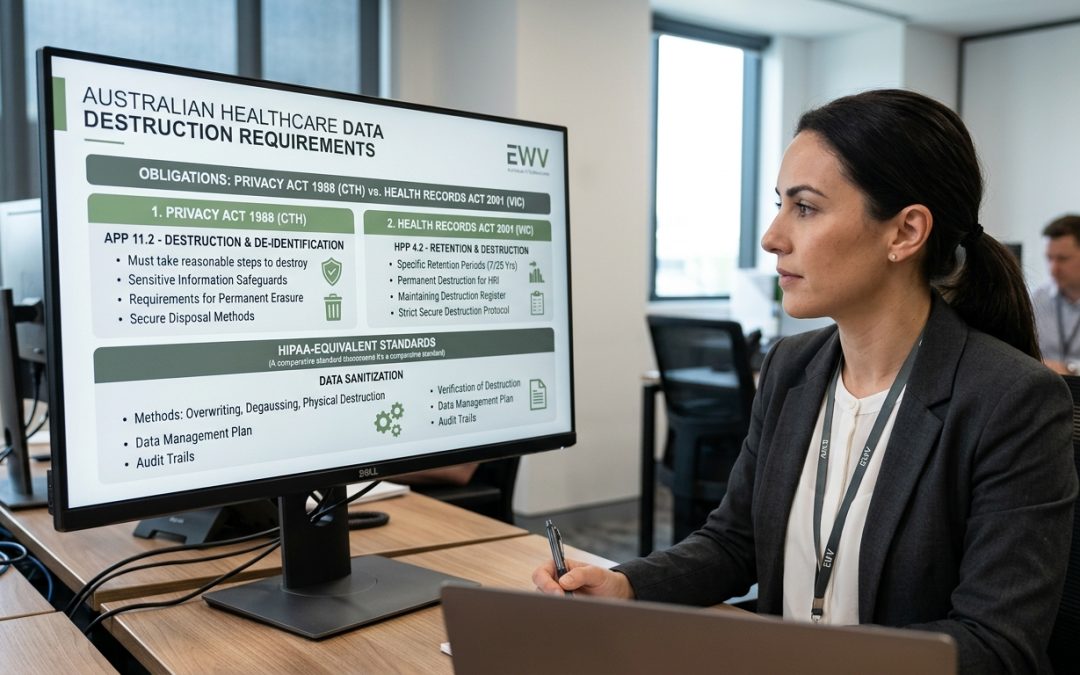
Australia has no HIPAA, but the Privacy Act, My Health Records Act and state health records laws all apply when you retire equipment that held patient data. Here is what they require.
How PCI DSS applies when you retire equipment that held cardholder data: the relevant requirements, which devices are in scope, accepted destruction methods and common audit findings.
What ADISA is, how its audits and forensic testing work, how it compares with ISO 27001, NIST SP 800-88 and AS 5377:2022, and what to check before relying on a provider’s ADISA claim.
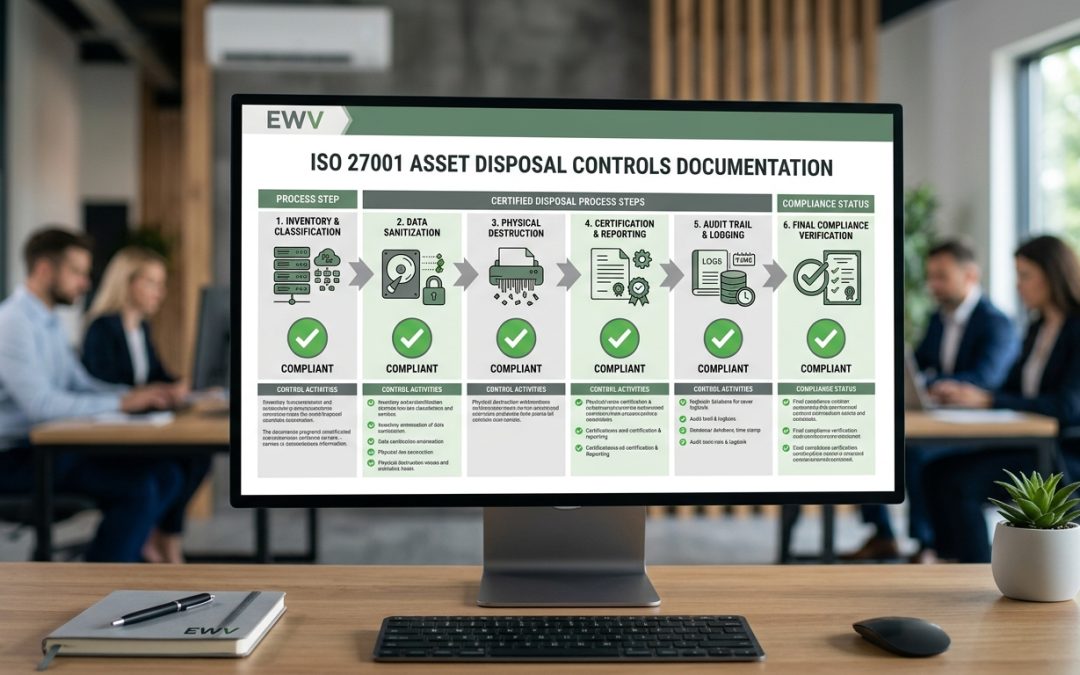
The ISO 27001:2022 Annex A controls that cover IT asset disposal, what auditors look for, how to match destruction methods to risk, and the non-conformities that come up most often.