
Hospitality Data Destruction: Hotel Guest Data
Hotels hold guest ID, payment and movement data on far more than the PMS. Here is where it sits, the Privacy Act and PCI DSS rules that apply, and how to dispose of it safely.
Hotels hold guest ID, payment and movement data on far more than the PMS. Here is where it sits, the Privacy Act and PCI DSS rules that apply, and how to dispose of it safely.
How pharmaceutical companies and CROs can destroy clinical trial and R&D data on retired IT equipment, balancing long TGA and GCP retention periods with privacy obligations.
How research institutions can destroy participant data, unpublished results and IP when retiring IT and lab equipment, in line with ethics approvals, funding conditions and privacy law.
How media organisations can protect unpublished content and confidential sources when retiring laptops, drives, memory cards and tape, with a tiered approach to destruction.
Why not-for-profits must destroy donor and client data properly when retiring IT equipment, how the Privacy Act applies, and how to build a simple disposal process on a tight budget.
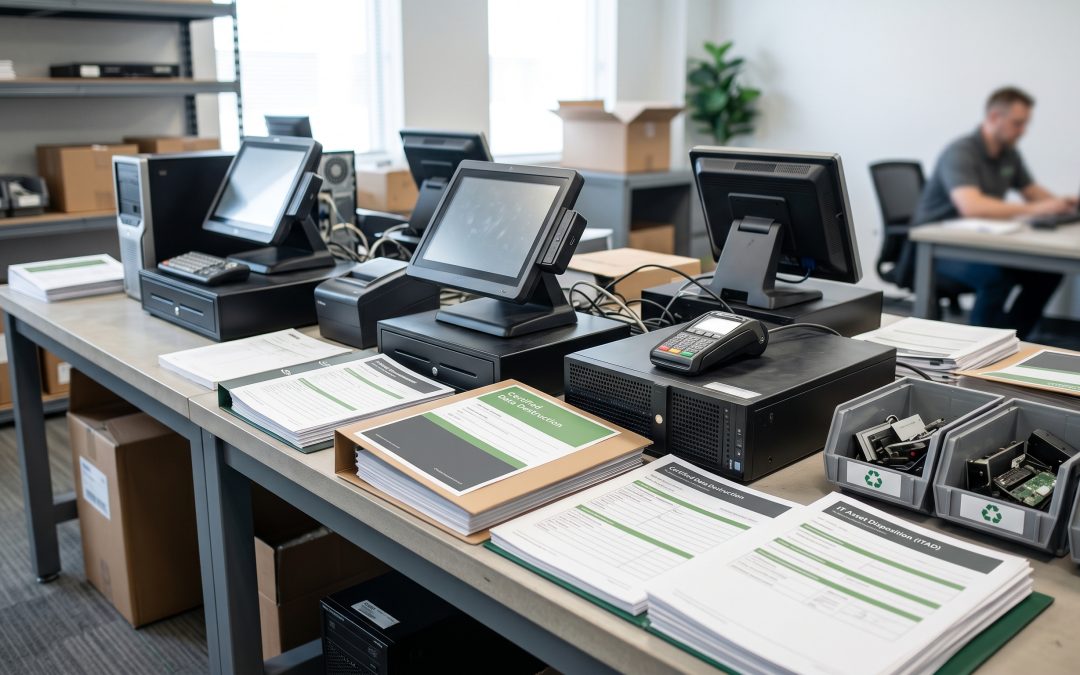
Where customer and card data sits on retail POS terminals, CRM servers and store devices, what the Privacy Act and PCI DSS expect, and a disposal workflow for multi-store retailers.