
Government Data Destruction: Classification and Requirements
How Australian government data must be destroyed at end of life, covering PSPF classifications, the ISM, NAA and PROV disposal authorities, clearances and contractor duties.
How Australian government data must be destroyed at end of life, covering PSPF classifications, the ISM, NAA and PROV disposal authorities, clearances and contractor duties.
How schools, universities and RTOs in Victoria should destroy student data on retired IT, covering privacy law, PROV and ESOS retention, children’s data and the landfill ban.
How APRA CPS 234, PCI DSS, the Corporations Act and AML/CTF rules shape data disposal for Australian financial services firms, from retention to audit-ready records.
How law firms should destroy client data on retired IT, covering legal professional privilege, Rule 9 confidentiality, retention checks, destruction standards and provider terms.
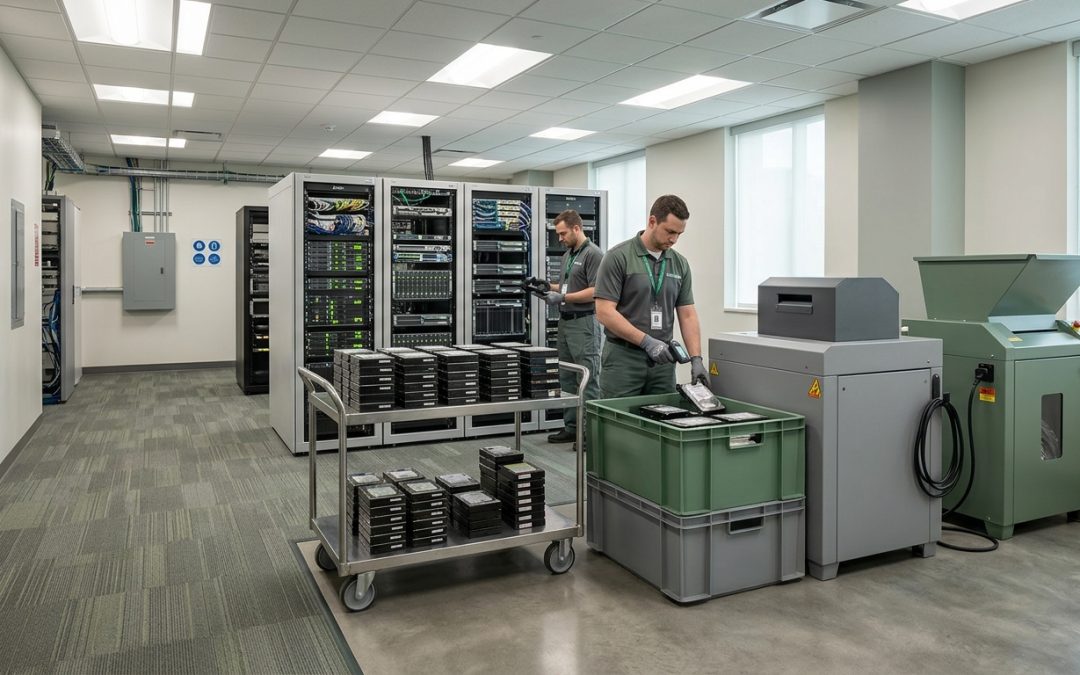
How Victorian healthcare providers should handle patient data on retired IT, from Health Records Act retention to imaging systems, Purge-level sanitisation and audit records.
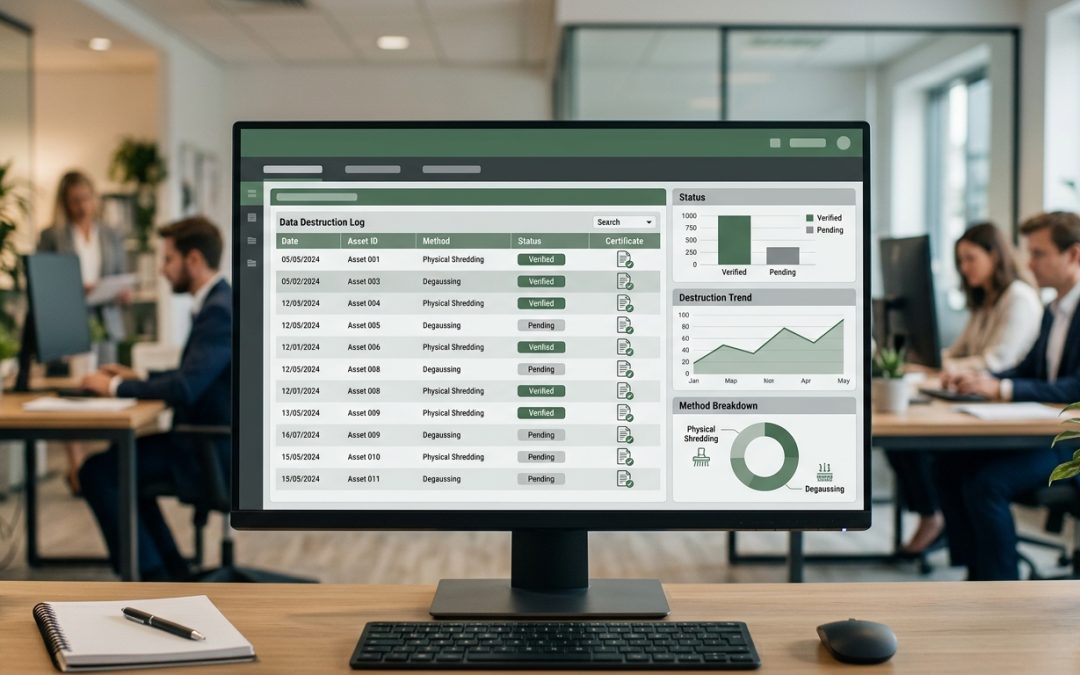
What a data destruction log and certificate should record, how to structure reporting, how long to keep records, and the documentation gaps that weaken audit evidence.